Financial institutions must move beyond paper-based compliance and adopt effective data protection measures to safeguard customer information and strengthen cybersecurity, thereby ensuring that Mauritius remains a trusted destination for financial services, stated the Minister of Information Technology, Communication and Innovation, Dr Avinash Ramtohul.

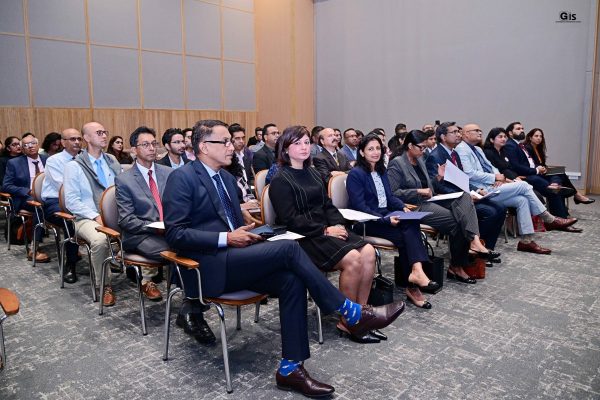




He was speaking this morning at the launch of the Guide on Data Protection in the Mauritian Financial Sector at the Shri Atal Bihari Vajpayee Tower, Ebène. The guide aims to promote robust data protection practices across Mauritius’ financial sector and underscores the importance of safeguarding personal information in an increasingly digital financial landscape.
The Governor of the Bank of Mauritius (BoM), Dr (Mrs) Priscilla Muthoora Thakoor; the Data Protection Commissioner, Mrs Drudeisha Madhub; representatives of the financial sector; and other personalities were present.
In his address, the Minister pointed out that only around 23,000 of the estimated 60,000 entities required to register as data controllers, data processors or data collectors had completed the registration process. He called on financial institutions to translate the newly launched guide into concrete action, stressing that protecting personal data is a shared responsibility that is essential to maintaining public trust, enhancing business resilience and ensuring the long-term competitiveness of Mauritius’ financial services sector.
He further underscored the need to strengthen the role of Data Protection Officers through specialised training, clearly defined qualification criteria and appropriate certification.
The Minister further highlighted the close interrelationship between the financial services and information technology sectors, which contribute approximately 13% and 5%, respectively, to the national economy. He stressed that both sectors play a pivotal role in driving economic growth and underscored the importance of upholding the highest standards of data protection. He emphasised that safeguarding personal information and maintaining public trust are shared responsibilities that require the commitment of all stakeholders.
He outlined the Government’s intention to propose the establishment of a dedicated Cybersecurity Agency and to review the Cybersecurity and Cybercrime Act 2021 to address emerging threats. Emphasising the need to protect critical information infrastructure, including banks and insurance companies, he called for more stringent security requirements and regular audits by qualified cybersecurity professionals.
Addressing the growing use of artificial intelligence (AI), the Minister called for a risk-based approach to AI governance, supported by robust safeguards for privacy, accountability and transparency. He stressed the need for stronger incident preparedness, effective data governance, cross-border cooperation and compliance with international standards to enhance the resilience and trustworthiness of the financial services sector.
Dr Muthoora Thakoor reaffirmed the BoM’s commitment to financial sector stability and soundness, warning that failure to meet regulatory requirements could undermine financial institutions and public confidence. The Governor of the BoM also stressed the importance of responsible data handling and safeguarding customer information amid digital transformation and evolving cyber threats.
The Data Protection Commissioner highlighted the financial sector’s responsibility to protect sensitive financial, transactional and behavioural data. She urged institutions to integrate data protection into decision-making, strengthen cybersecurity, conduct Data Protection Impact Assessments, ensure the responsible use of artificial intelligence, and improve oversight of third-party providers and cross-border data transfers.
Date: 29 October 2026
Source: GIS News
Topics: Financial Services